Entropy Shield
Entropy Shield is Maze's anonymity stack in one place. Instead of wiring Tor,
encrypted DNS and I2P together yourself — editing torrc, writing nftables
rules, restarting services — you turn them on from one window, and it puts
everything back the way it was when you disconnect.
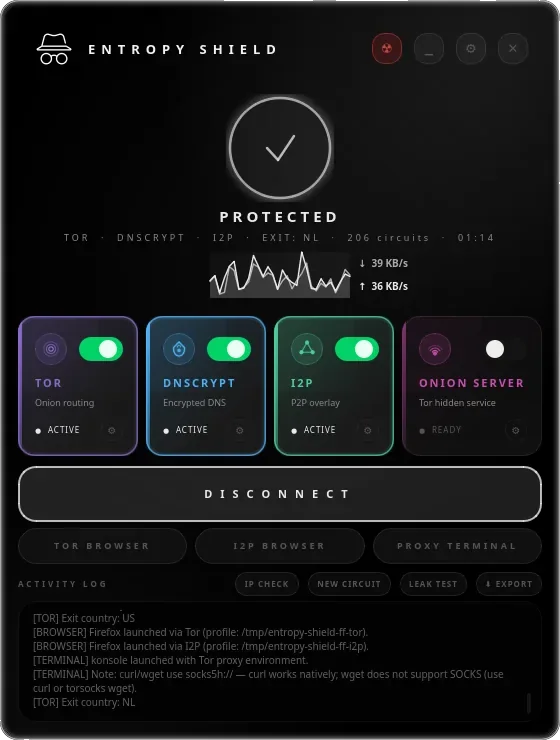
It does not connect by default. Entropy Shield is installed, but nothing is routed through Tor until you press Connect. After the first launch it starts hidden in the tray at login; Auto-connect is off unless you turn it on. (The
torservice that is enabled at boot is only a SOCKS proxy that apps must be pointed at.)
What it can turn on
Pick any combination:
| Layer | What it does |
|---|---|
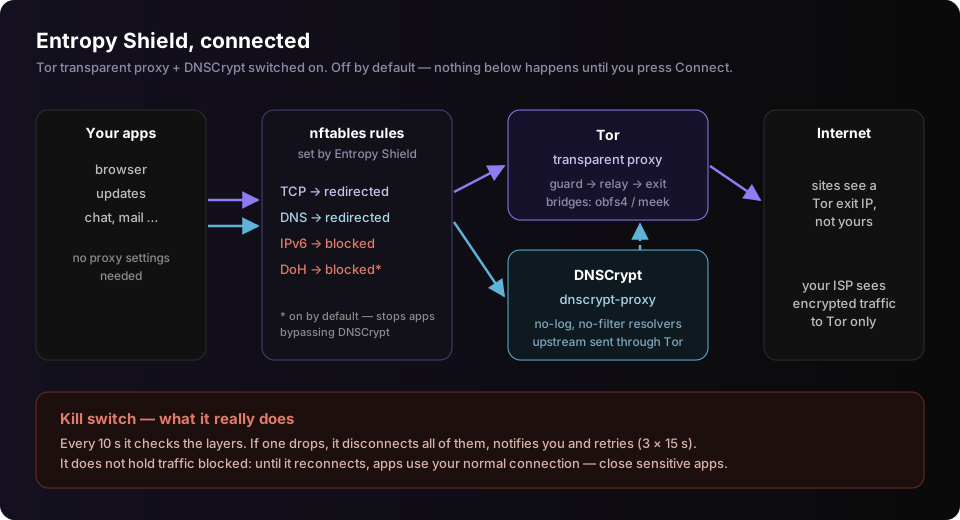
| Tor transparent proxy | Routes all TCP traffic of the system through Tor (nftables redirect), DNS through Tor's DNS port. All IPv6 is blocked meanwhile, because Tor's transparent port is IPv4-only |
| DNSCrypt | Encrypts DNS with dnscrypt-proxy (no-log, no-filter servers only) and redirects IPv4 and IPv6 DNS to it. With Tor on too, dnscrypt-proxy sends its queries through Tor |
| I2P (i2pd) | Starts i2pd and its HTTP/SOCKS proxies; combined with Tor, I2P traffic tunnels through Tor |
| Onion server | Publishes a local folder as a Tor hidden service (.onion address) |
dnscrypt-proxyandi2pdare installed as Entropy Shield's dependencies, but neither is enabled as a standalone service — Entropy Shield starts and stops them.
Kill switch and leak protection
The kill switch (on by default) checks the active layers every 10 seconds. If one of them drops — Tor or dnscrypt-proxy stops — Entropy Shield disconnects every layer, shows a Kill Switch notification, and tries to reconnect (3 attempts, 15 seconds apart; set in Settings).
It does not hold your traffic blocked. Disconnecting removes Entropy Shield's firewall rules, so until it reconnects your apps use your normal connection. If you cannot afford a single unprotected request, close sensitive apps when you see the notification, or use Tor Browser, which never falls back to a direct connection.
While connected it also applies IPv6 leak protection (all IPv6 is blocked under Tor), blocks DNS-over-HTTPS by default so apps cannot bypass DNSCrypt, and has a built-in leak test (Tor exit, DNS, IPv6, WebRTC, time zone, hostname).
More
- Tor bridges — obfs4, meek-azure or your own bridge lines, for networks
that block Tor (
obfs4proxyis preinstalled). Snowflake is not supported: its client is not packaged for Arch. - New identity on a timer — rotates your Tor circuit every N minutes.
- Per-app routing — send chosen applications through Tor, direct, or block them.
- MAC randomization on connect — optional; if you already use Maze Cloak, let one of the two own the MAC address.
- Isolated browser profiles — Firefox profiles pre-configured for Tor or I2P that share nothing with your everyday profile.
- Themes — OLED, Light, Binary, Circuit and Pixel; minimises to the tray.
Running it
entropy-shield # or launch it from the application menu
The window runs as your normal user; the privileged work is done by
entropy-shield.service (root), which it talks to over a group-restricted
socket — no password prompts.